Security leadership, minus the noise.
Field notes on cyber risk, GRC and AI from a practising CISO in the UAE — written for people who have to make the call on Monday morning.
-
From ISO 27001 to ISO 42001
This is practical guidance. It is not the text of ISO/IEC 27001:2022 or ISO/IEC 42001:2023, and it is not a certificate. Zaheer Ikbal, Founder, CyHelm For years, ISO/IEC 27001:2022 has been the…
This week · Cyber Pulse
-
Cyber Pulse: Week 40, 2026
Read the brief →: Cyber Pulse: Week 40, 2026Four vendors confirmed that new flaws were being exploited: Fortinet FortiMail, Cisco Catalyst SD-WAN Manager, Citrix NetScaler (SAML) and Apple CoreGraphics.
Explore by topic
AI & Cybersecurity
Local LLMs, AI threats, and securing AI in the enterprise.
Compliance & Governance
ISO 27001, UAE PDPL, NESA/IAS and audit-ready programmes.
CISO & Leadership
Board reporting, budgets, and aligning security with business.
Threats & Trends
Ransomware economics, malware-free attacks and threat intelligence.
Zero Trust & Architecture
SASE, CNAPP, network design and building for assumed breach.
Latest analysis
-
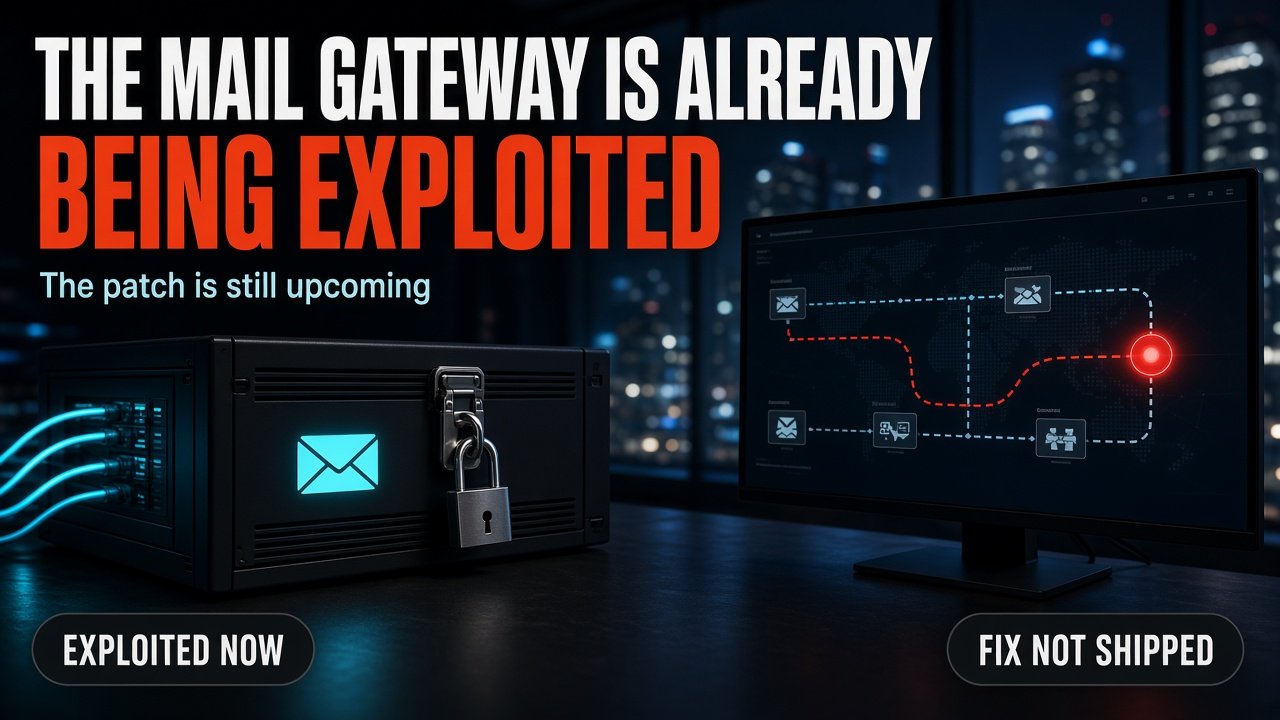
The mail gateway is already being exploited. The patch is still upcoming.
Zaheer Ikbal, Founder, CyHelm I would not sit on this one waiting for a patch note. Fortinet published FG-IR-26-175 on 1 October.…
-
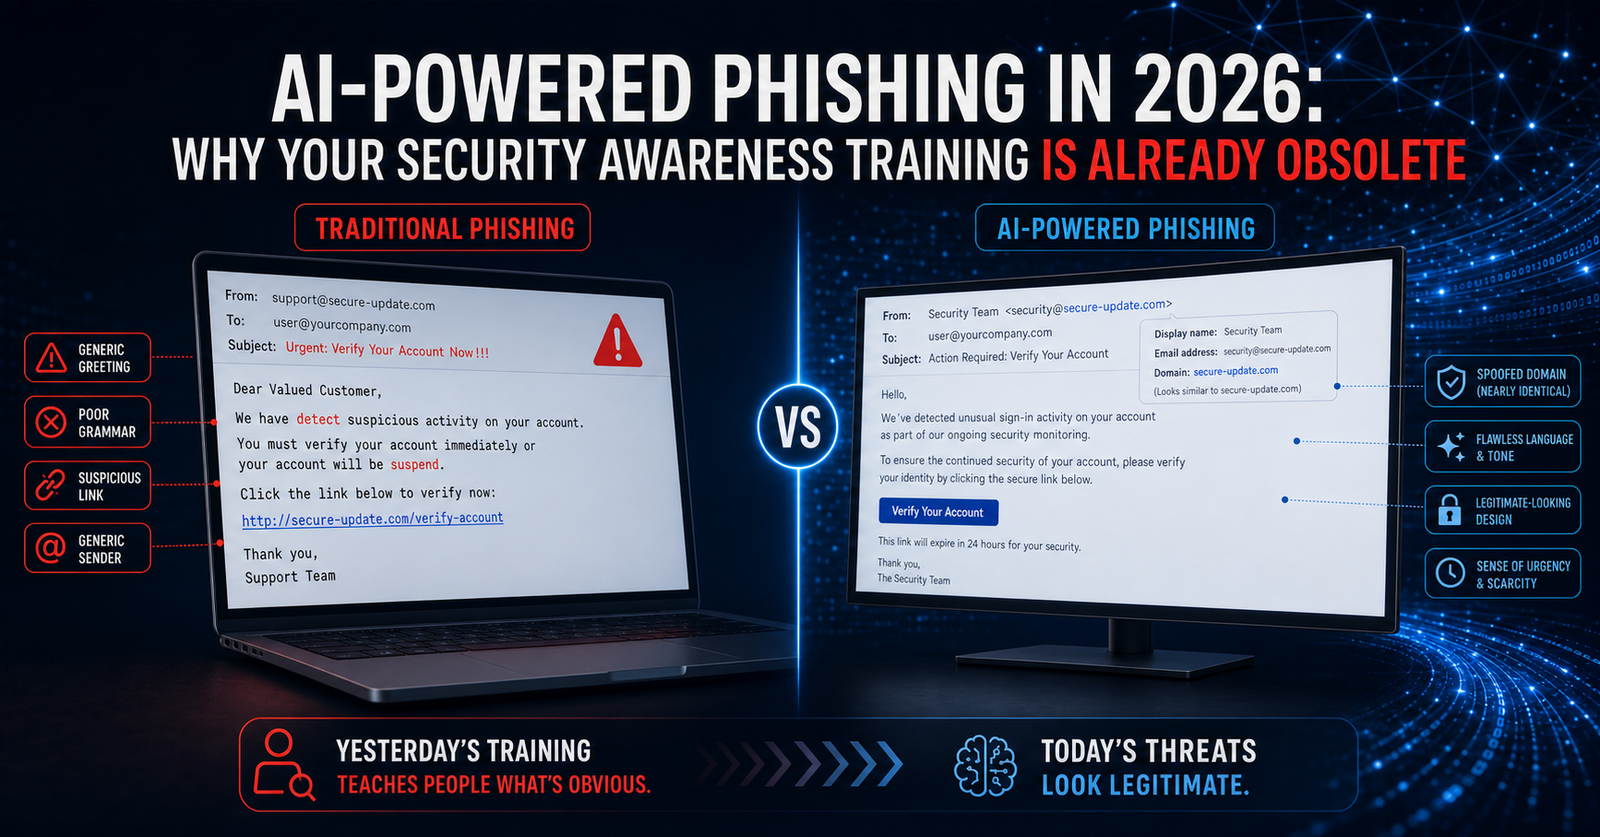
AI-Powered Phishing in 2026: Why Your Security Awareness Training Is Already Obsolete
AI-written lures now beat phishing simulations. Why click-rate metrics mislead boards, and the 5-layer defence model CISOs should adopt in 2026.
-
Running LLMs Locally in 2026 — The Best Options, Tools & Comparison Chart
Run AI on your own hardware: Llama 4, Qwen3, DeepSeek, Gemma 3 and Phi-4 compared, plus Ollama and LM Studio and the…
-
The Ultimate Guide to Threat Intelligence Platforms in 2026: Tools Every Security Team Needs
Cyber threats are evolving faster than any single analyst can track. Ransomware gangs retool overnight, nation-state actors shift infrastructure in hours, and…
-
ISO/IEC 27001 – Introduction and Practical Guidance
In a world of constant cyber threats, ISO/IEC 27001 has become the global reference point for building and proving an effective information…
-
ISO 27001 Implementation Lessons from the UAE — What They Don’t Tell You in the Textbook
Let me be honest with you. I’ve been through ISO 27001 implementations in the UAE, and I can tell you that the…
Start here
For CISOs & boards
Run security like a business function
For GRC & compliance
Get audit-ready without the theatre
For practitioners
Stay ahead of the attacker
The Monday Brief
Ten minutes on Monday. Ready for the week.
- Top threats and actively exploited CVEs, ranked by real risk
- Regulation watch for the UAE & GCC (PDPL, NESA/IAS, CBUAE)
- One practical playbook or template you can use the same day
No spam — unsubscribe in one click. See our privacy policy.
Written by a practitioner
Zaheer Ikbal
20+ years building security programmes for enterprises in the UAE. Everything here comes from real implementations, audits and incidents — not vendor brochures.
CCISO · CISSP · CISM · CISA · CEH · MBA